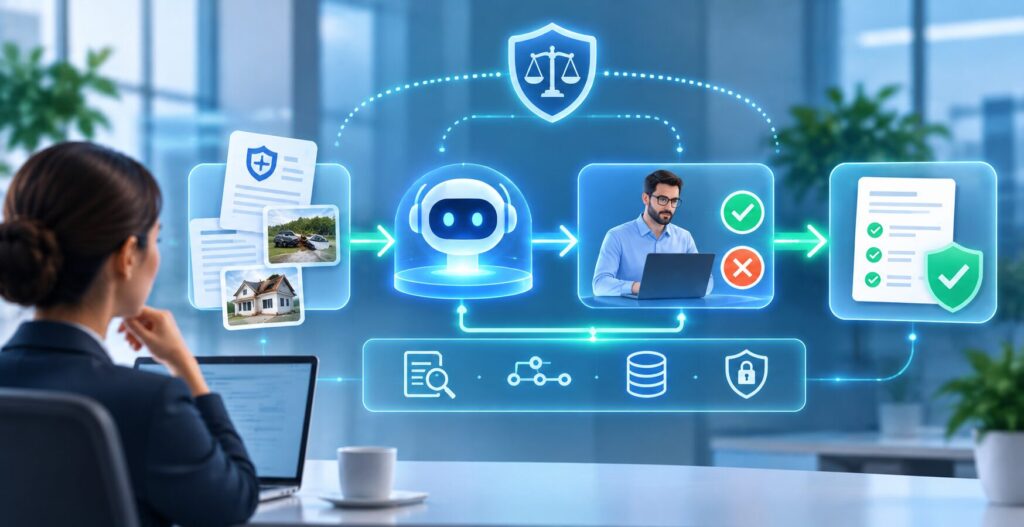
Insurance companies can build auditable AI workflows in insurance by recording data inputs, model versions, AI outputs, human reviews, approvals, and final actions. They should establish risk-based oversight, maintain traceable audit logs, validate model performance, monitor exceptions, and ensure authorized employees can challenge or override AI recommendations before consequential decisions are made.
Executive Summary
Insurance companies are increasingly using artificial intelligence (AI) to improve underwriting, claims processing, fraud detection, policy servicing, customer engagement, and operational decision-making. However, deploying AI successfully requires more than achieving model accuracy or automating repetitive tasks. Insurers must also be able to explain how AI systems operate, demonstrate how decisions are reviewed, and establish who is accountable for the outcomes.
This is particularly important in insurance, where AI-supported decisions can influence policy eligibility, pricing, claims outcomes, fraud investigations, customer communications, and other activities that affect consumers.
An AI workflow may produce a recommendation in seconds, but insurers need to answer several important questions:
- What information did the AI system use?
- Which model, version, and business rules influenced the output?
- Was the recommendation reviewed by an authorized employee?
- Could the reviewer challenge, correct, or override the recommendation?
- What action was ultimately taken?
- Can the organization reconstruct the entire process later?
- Who is responsible if the workflow produces an inaccurate or unfair outcome?
These questions define the need for auditable AI workflows with human oversight.
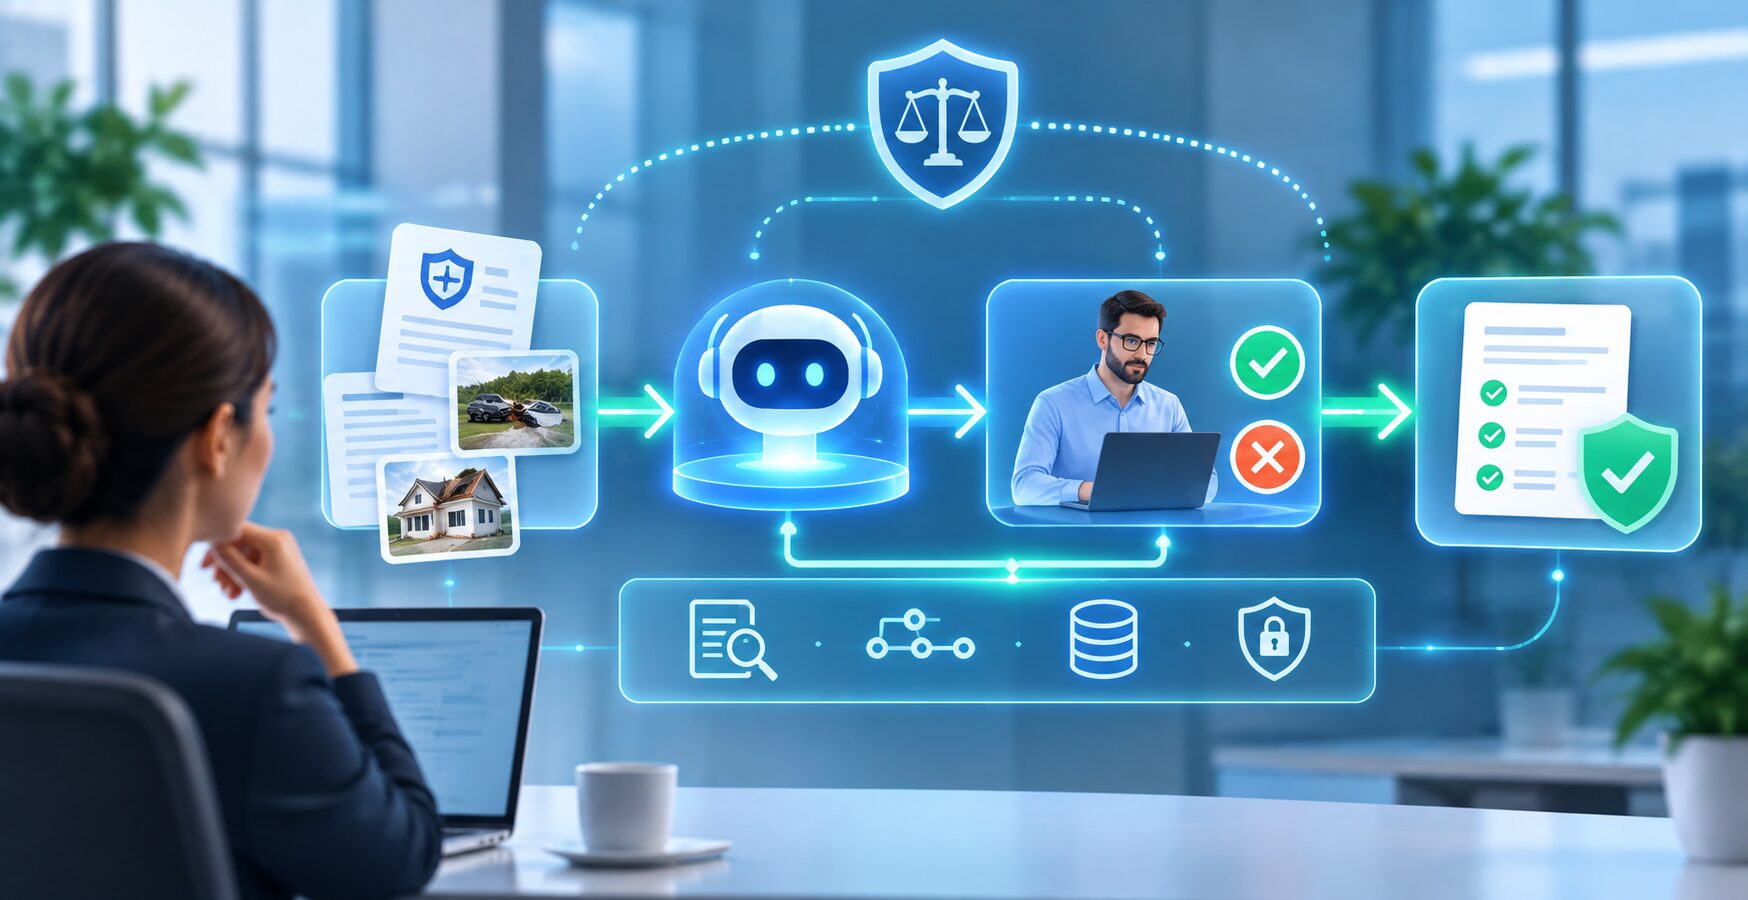
An auditable AI workflow maintains traceable evidence across the complete decision lifecycle. It records relevant inputs, model and system versions, AI outputs, human interventions, approvals, exceptions, and final actions. Human oversight ensures that people with appropriate authority and expertise can evaluate AI recommendations, intervene when necessary, and remain accountable for decisions.
Building this capability requires a combination of AI governance, workflow orchestration, model monitoring, data lineage, access controls, audit logging, human review mechanisms, and clearly defined accountability.
For insurers, the objective is not to prevent AI from automating work. It is to make automation controlled, explainable, measurable, and accountable.
This article explains how insurance companies can design auditable AI workflows, implement meaningful human oversight, establish governance controls, and scale AI adoption without losing operational accountability.
TL;DR
Insurance companies can build auditable AI workflows by integrating governance, traceability, human review, and continuous monitoring into every stage of AI-enabled operations.
A reliable approach includes:
- Maintaining an inventory of AI models, agents, vendors, and use cases.
- Classifying AI workflows according to business and consumer impact.
- Recording input data, model versions, prompts, outputs, and actions.
- Defining clear human approval and escalation requirements.
- Providing reviewers with evidence, context, and override authority.
- Maintaining audit trails for AI recommendations and final decisions.
- Testing for accuracy, bias, security, and reliability.
- Monitoring model drift, workflow exceptions, and human intervention patterns.
- Establishing third-party AI governance and vendor accountability.
- Reviewing and updating controls throughout the AI lifecycle.
The result is an insurance AI environment where automation remains traceable, human judgment remains meaningful, and business decisions can be reconstructed and reviewed.
Introduction: Why AI Needs Human Oversight and Auditability in Insurance and
AI is changing how insurance companies process information and make operational decisions.
Underwriters can use AI to summarize applications and identify risk indicators. Claims teams can use AI to extract information from documents, classify claims, and recommend next steps. Fraud teams can use predictive models to identify suspicious patterns. Customer service teams can use generative AI to retrieve policy information and draft responses.
These applications create opportunities to improve speed, productivity, and service quality.
However, insurance decisions are not ordinary automation tasks. They operate within regulated business processes where accuracy, fairness, consumer protection, data privacy, and accountability matter.
Consider an AI-enabled claims workflow.
A policyholder submits a claim with photographs, supporting documents, and an incident description. An AI system extracts relevant information, summarizes the incident, checks policy details, identifies missing documents, and recommends a next action.
The workflow may appear straightforward. But several questions arise:
- Did the system retrieve the correct policy version?
- Did it identify all relevant documents?
- Did it interpret the coverage conditions correctly?
- Did it distinguish between missing information and a coverage exclusion?
- Was its recommendation reviewed by an authorized claims professional?
- Was the final decision recorded with an explanation?
If the system recommends an incorrect action and the organization cannot reconstruct how that recommendation was produced or reviewed, the problem extends beyond model performance.
It becomes an issue of operational control and accountability.
This is why insurers need to move from isolated AI applications toward governed AI workflows.
The goal is to ensure that every consequential AI-supported process has a defined purpose, approved data sources, controlled system behavior, meaningful human oversight, and a traceable decision record.
Read our blog on P&C Insurance Data Management: Build a Trusted Data Foundation
What Is Auditable AI Workflows in Insurance?
An auditable AI workflow is an AI-enabled business process that records the relevant information, system behavior, human interventions, approvals, and final actions required to reconstruct and review how a task or decision was completed.
In insurance, an auditable workflow connects AI activity with business processes such as underwriting, claims management, fraud investigation, policy servicing, and customer communication.
It should make the following information available:
- Workflow context: What business process was being performed and why?
- Input information: What data, documents, and records were used?
- AI system details: Which model, version, configuration, and tools were involved?
- Output evidence: What recommendation, classification, summary, or action did the system produce?
- Human involvement: Who reviewed, approved, rejected, or modified the recommendation?
- Decision rationale: What evidence and rules supported the final action?
- Execution record: What action was ultimately performed?
- Monitoring evidence: Were errors, exceptions, overrides, or unusual patterns identified?
An audit trail should not be confused with a simple application log.
A technical log may record that an API was called or a model returned a response. An auditable workflow must connect that technical activity to the business process, applicable controls, human decision, and resulting action.
For example, recording that an AI model classified a claim as high priority is not enough. The organization should also be able to establish which claim information was available, which model version produced the classification, whether a claims professional reviewed it, and what action followed.
The key principle: An auditable AI workflow must preserve evidence of both automated activity and human accountability.
Why Human Oversight and Auditability in Insurance Matter
Auditability and human oversight help insurers manage the risks created when AI systems influence operational and consumer-impacting decisions. They provide evidence of how AI was used, establish accountability, support internal controls, and help organizations investigate errors or unexpected outcomes.
1. Insurance Decisions Can Directly Affect Consumers
AI can influence decisions involving policy eligibility, pricing, claims handling, fraud referrals, and customer communications.
An inaccurate recommendation may lead to an inappropriate escalation, delayed processing, incorrect customer information, or an unfair outcome.
Human oversight provides a mechanism to evaluate recommendations before they influence important business actions.
2. Regulators Expect Insurers to Govern AI Use
Insurance regulators increasingly expect companies to understand and manage the AI systems they use.
The National Association of Insurance Commissioners (NAIC) adopted its Model Bulletin on the Use of Artificial Intelligence Systems by Insurers in December 2023.
The bulletin describes expectations around AI governance and the information regulators may request when examining insurers’ use of AI. This includes documentation relating to models, data sources, validation, testing, auditing, and third-party systems.
The bulletin is a model supervisory document. Its legal effect depends on adoption and applicable requirements in individual jurisdictions.
3. AI Outputs Need Context and Verification
AI systems can produce inaccurate, incomplete, or misleading outputs. Generative AI may also generate information that appears convincing but is not supported by the underlying evidence.
In insurance, this can create problems when AI-generated summaries, recommendations, or explanations are treated as verified business facts.
A controlled workflow should preserve the evidence behind an output and provide an appropriate review mechanism.
4. Accountability Cannot Be Delegated to a Model
An AI system can generate a recommendation, but it does not become the accountable business owner of an insurance decision.
Insurers remain responsible for ensuring that AI-supported activities comply with applicable laws, regulations, and internal policies.
Human oversight, defined responsibilities, and documented approval processes help maintain this accountability.
Read our blog on Insurance Legacy System Modernization: A Practical Guide
5. Auditable Workflows Make AI Easier to Scale
Organizations often begin with small AI pilots. However, scaling an application across multiple departments introduces additional complexity.
Different teams may use different models, data sources, prompts, approval mechanisms, and operating procedures.
A standardized audit and oversight framework creates reusable controls that can support AI adoption across the enterprise.
Understanding Human Oversight: Human-in-the-Loop, Human-on-the-Loop, and Human-in-Command
Human oversight is not a single approval step. It can take different forms depending on the risk, autonomy, and intended use of an AI workflow.
Three useful design patterns are human-in-the-loop, human-on-the-loop, and human-in-command.
| Oversight pattern | How it works | Insurance example |
|---|---|---|
| Human-in-the-loop | A person reviews or approves an AI output before a defined action proceeds | A claims professional reviews an AI-generated recommendation before a consequential claims decision |
| Human-on-the-loop | A person supervises an automated workflow and can intervene when necessary | A fraud analyst monitors AI-generated alerts and investigates unusual patterns |
| Human-in-command | People retain authority over the system’s purpose, operating boundaries, governance, and deployment | An AI governance committee approves permitted use cases, risk limits, and deployment conditions |
These are architectural and operational patterns, not interchangeable regulatory definitions.
When Should Human-in-the-Loop Be Used?
Human-in-the-loop is appropriate when an AI output needs an authorized person to review or approve it before the workflow can proceed.
Examples include:
- Reviewing AI-assisted underwriting recommendations.
- Approving high-impact claims decisions.
- Reviewing potentially adverse customer communications.
- Confirming fraud investigation escalations.
- Approving changes to policy information that require authorization.
The reviewer should receive enough information to understand the recommendation and evaluate its validity.
When Should Human-on-the-Loop Be Used?
Human-on-the-loop is appropriate when an automated process operates within defined limits, while a person monitors its performance and can intervene when conditions require attention.
Examples include:
- Monitoring automated document classification.
- Reviewing exceptions in claims routing.
- Supervising automated data extraction.
- Monitoring fraud detection alerts.
- Identifying unusual patterns in AI-generated customer service interactions.
Monitoring should include defined intervention triggers rather than relying only on passive observation.
Why Is Human-in-Command Important?
Human-in-command establishes organizational control over AI systems.
It ensures that the organization determines:
- Which business processes can use AI.
- Which decisions must remain under human authority.
- What data and models are permitted.
- What risk levels are acceptable.
- Who can approve deployment.
- When a model or workflow must be suspended.
- Who is accountable for system performance.
Without this level of control, human review may exist at the individual workflow level while the organization lacks effective oversight of the overall AI environment.
Common Insurance Use Cases That Require Auditable AI Workflows
AI auditability should be designed around the actual business process, not implemented as a generic logging feature.
Different insurance workflows have different risks, review requirements, and evidence needs.
1. AI-Assisted Underwriting
AI can help underwriters review applications, summarize risk information, extract details from supporting documents, and identify missing information.
An auditable underwriting workflow should record:
- Application and supporting document references.
- Relevant policy and risk information.
- Approved data sources.
- Model and system versions.
- Extracted risk attributes.
- AI-generated summaries and recommendations.
- Human review and modifications.
- Final underwriting action and authorized approver.
Human oversight: An authorized underwriter should evaluate recommendations according to the applicable underwriting rules and authority framework. AI should not independently make restricted decisions outside its approved scope.
2. AI-Assisted Claims Processing
Claims workflows may use AI for document extraction, claim categorization, missing-information detection, prioritization, and recommendation generation.
An auditable claims workflow should capture:
- Claim identifier and relevant policy version.
- Submitted documents and source references.
- Extracted information.
- Applicable coverage information.
- AI classification and recommendation.
- Exceptions or uncertainty indicators.
- Human review and corrections.
- Final claims action.
Human oversight: Claims professionals should review consequential recommendations, especially where coverage interpretation, disputed information, customer impact, or complex circumstances require professional judgment.
3. AI-Based Fraud Detection
AI models can analyze claims, transactions, relationships, and historical patterns to identify potentially suspicious activity.
An auditable fraud workflow should capture:
- Data used for risk assessment.
- Model version and relevant features.
- Risk scores and alert reasons.
- Thresholds and decision rules.
- Supporting evidence.
- Analyst review and investigation notes.
- Escalation and final disposition.
Human oversight: A fraud alert should not automatically be treated as proof of fraud. Qualified investigators should evaluate the available evidence before taking consequential action.
4. AI-Powered Customer Service
Generative AI assistants can retrieve policy information, summarize customer requests, draft responses, and support service representatives.
An auditable customer service workflow should record:
- Customer request and relevant interaction context.
- Approved knowledge sources.
- Retrieved policy or product references.
- Model and prompt configuration.
- Generated response.
- Human edits or approval, where required.
- Final response delivered to the customer.
Human oversight: Customer service teams should review sensitive, disputed, or complex responses and have a clear process for escalation to qualified personnel.
5. AI-Assisted Document Processing
Insurance companies process applications, inspection reports, medical documents, invoices, repair estimates, and other supporting records.
AI can extract information and route documents to appropriate teams.
An auditable document workflow should record:
- Original document reference.
- Document classification.
- Extracted fields.
- Confidence or uncertainty information, where available.
- Validation results.
- Human corrections.
- Downstream system updates.
Human oversight: Low-confidence extraction, missing information, conflicting records, and sensitive documents should trigger appropriate review.
6. AI Agents for Insurance Operations
AI agents can perform multi-step activities such as retrieving information, checking workflow status, preparing summaries, and initiating permitted actions through enterprise systems.
These workflows require additional controls because agents may call tools, access multiple data sources, and perform actions beyond generating text.
An auditable agent workflow should record:
- Agent identity and version.
- User or system initiating the task.
- Task objective and authorized scope.
- Data sources accessed.
- Tools and APIs invoked.
- Actions proposed and executed.
- Permission checks.
- Human approvals and overrides.
- Final workflow status.
Human oversight: High-impact or irreversible actions should require explicit authorization according to the organization’s risk and approval policies. Agent permissions should follow least-privilege principles.
How to Build an Auditable AI Workflow Architecture
An auditable AI architecture should connect the data layer, AI services, workflow orchestration, human review, business applications, and governance controls.
Auditability must be designed into the workflow from the beginning rather than added after deployment.
1. Establish an AI System Inventory and Governance Framework
Before designing individual workflows, insurers should understand which AI systems are already in use.
An AI inventory should include:
- AI application or workflow name.
- Business owner.
- Technical owner.
- Intended purpose.
- Business process supported.
- Model and vendor information.
- Data sources.
- Consumer or operational impact.
- Risk classification.
- Human oversight requirements.
- Approval status.
- Monitoring and review frequency.
The inventory should include internally developed models, commercial AI services, embedded vendor AI capabilities, generative AI applications, and AI agents.
This is important because AI may be used indirectly through third-party applications or technology platforms.
Practical recommendation: Create a centralized AI registry and establish an approval process for new AI use cases, material model changes, and changes in intended use.
2. Classify AI Workflows by Risk and Business Impact
Not every AI workflow requires the same level of human intervention.
A document summarization assistant and an AI-supported claims decision workflow should not automatically receive identical controls.
A risk classification framework can consider:
- Consumer impact.
- Financial impact.
- Regulatory relevance.
- Potential for unfair discrimination.
- Data sensitivity.
- Degree of automation.
- Reversibility of the action.
- Model uncertainty.
- Availability of human review.
- Third-party dependencies.
An illustrative risk-tiering framework is shown below.
| Risk tier | Example workflow | Suggested control approach |
|---|---|---|
| Low | Internal document summarization | Approved data sources, access controls, logging, periodic sampling |
| Moderate | Claims document classification and routing | Quality thresholds, exception handling, human review of uncertain cases, monitoring |
| High | AI-supported underwriting or consequential claims recommendations | Enhanced validation, documented human approval, explainability evidence, formal monitoring |
| Restricted or prohibited | Use cases outside approved legal, ethical, or organizational boundaries | Block deployment or require formal legal and governance review before any permitted use |
This framework is illustrative. Insurers should define their own risk categories based on applicable regulations, business impact, and internal risk appetite.
Practical recommendation: Apply controls proportionately. Higher-impact workflows should have stronger validation, more detailed evidence, clearer approval authority, and more frequent monitoring.
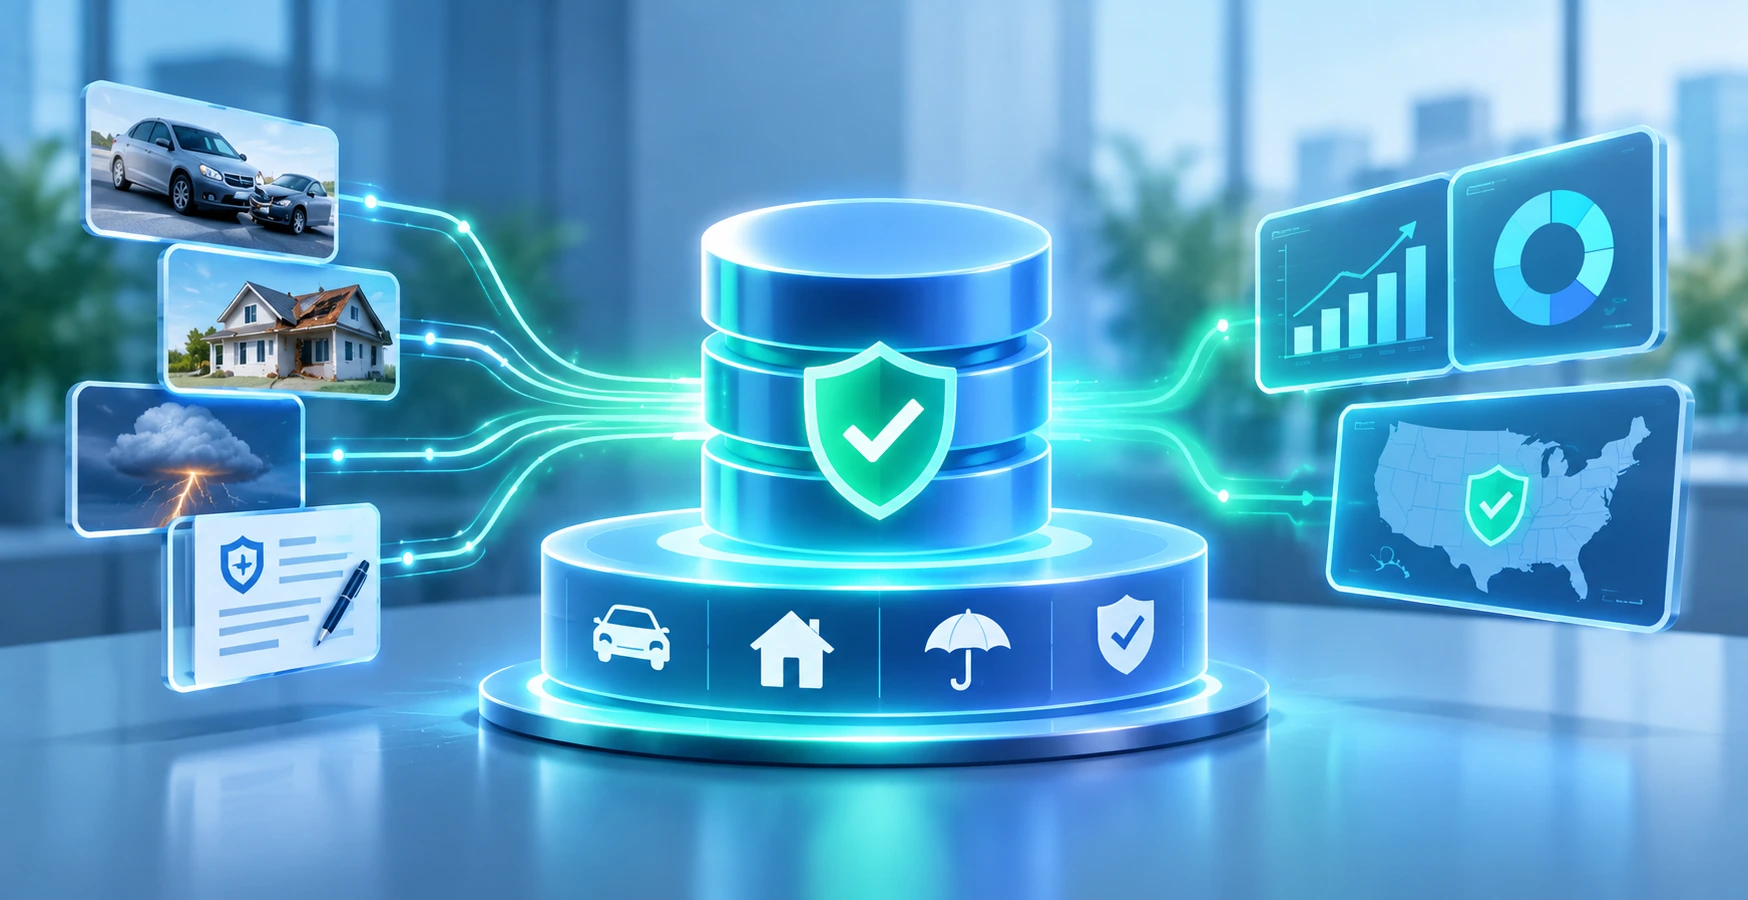
3. Establish Trusted Data Sources and Data Lineage
AI systems can produce unreliable results when they use incomplete, outdated, inaccurate, or inappropriate data.
An auditable workflow should identify which data sources are authorized for each use case.
For insurance applications, these may include:
- Policy administration systems.
- Claims management platforms.
- Billing and financial systems.
- Approved underwriting data.
- Customer records.
- Enterprise document repositories.
- External risk and enrichment providers.
- Approved knowledge bases.
The system should also maintain information about data provenance and transformation.
For example, an AI-generated claims summary should be traceable to the relevant claim documents and approved policy information.
For retrieval-augmented generation (RAG) workflows, the audit record should include the retrieved document references or identifiers, retrieval context, and relevant knowledge-base version.
Practical recommendation: Use governed data products, documented source mappings, access controls, and data lineage capabilities. Do not allow an AI workflow to silently retrieve information from unauthorized or unverified sources.
4. Record Model, Prompt, and Configuration Versions
An AI output can change when the model, prompt, retrieval configuration, system instructions, or underlying data changes.
Without version information, an organization may be unable to reproduce or investigate a historical result.
For each relevant execution, capture:
- Model provider and model identifier.
- Model version or deployment identifier, where available.
- Prompt or instruction template version.
- Retrieval configuration.
- Relevant business rules.
- Tool and API versions.
- Workflow configuration.
- Timestamp and execution identifier.
- Applicable evaluation or approval status.
For generative AI, the exact output may not be reproducible even when the same model and prompt are used. Model behavior may also change through provider updates.
Therefore, auditability should focus on preserving the actual execution evidence, not assuming that the model can generate the same response again later.
Practical recommendation: Maintain a version-controlled configuration registry and link each AI execution to the exact available version metadata.
5. Implement Centralized Audit Logging
Centralized audit logging provides a structured record of AI workflow activity.
A useful audit record should connect technical execution with business context.
| Audit field | What it records |
|---|---|
| Workflow ID | Unique identifier for the workflow execution |
| Business case ID | Relevant claim, policy, application, or service request |
| User or initiating system | Who or what initiated the workflow |
| Timestamp | When each significant event occurred |
| Input references | Data and documents used |
| Model information | Model provider, identifier, and version |
| Prompt/configuration version | Instructions and settings applied |
| AI output | Recommendation, classification, summary, or generated response |
| Confidence or uncertainty | Relevant model indicators, where available |
| Validation results | Checks and policy rules applied |
| Human reviewer | Authorized person involved in the review |
| Human action | Approved, rejected, modified, or escalated |
| Final outcome | Action taken by the business workflow |
| Exception details | Errors, overrides, and escalation information |
Audit logging should also include access and security events where relevant.
However, logging should not become uncontrolled duplication of sensitive information. Insurers need to consider privacy, data minimization, encryption, retention, access controls, and secure handling of customer information.
For sensitive records, logs may store secure references, hashes, metadata, or controlled snapshots rather than unrestricted copies of all underlying documents.
Practical recommendation: Establish an enterprise audit logging standard with defined event schemas, retention requirements, access permissions, and monitoring.
6. Integrate Human Review Into Workflow Orchestration
Human oversight should be an operational workflow capability.
A review step should not simply display an AI recommendation and provide an approval button.
Reviewers need access to:
- The original request or business record.
- Relevant supporting documents.
- AI-generated output.
- Source references and evidence.
- Applicable business rules.
- Uncertainty or confidence indicators, where meaningful.
- Previous workflow actions.
- Available override and escalation options.
A reviewer should be able to:
- Approve the recommendation.
- Reject the recommendation.
- Modify the suggested output.
- Request additional information.
- Escalate the case.
- Stop the workflow.
The system should record the reviewer’s identity, action, timestamp, and reason where required.
It should also prevent unauthorized users from approving decisions outside their delegated authority.
Practical recommendation: Build human review into the workflow engine or business process platform rather than implementing separate approval logic in every AI application.
7. Establish Approval Gates for Consequential Actions
Certain actions should not execute automatically without the required authorization.
Examples include:
- Finalizing consequential claims decisions.
- Issuing restricted underwriting decisions.
- Initiating certain policy changes.
- Sending sensitive or disputed customer communications.
- Escalating potentially fraudulent cases into formal investigations.
- Executing financial transactions.
- Making changes to important customer or policy records.
Approval gates should be based on business rules, risk classification, authority limits, and applicable legal requirements.
An approval gate should define:
- Which action requires approval.
- Who is authorized to approve it.
- What evidence must be presented.
- Whether additional review is required.
- What happens if approval is rejected or delayed.
- How the final action is recorded.
Practical recommendation: Separate AI recommendation permissions from business action permissions. An AI service may be allowed to prepare a recommendation without having permission to execute the final action.
8. Implement Model and Workflow Monitoring
Auditability does not end after deployment.
AI performance can change because of new data patterns, changes in business processes, model updates, external conditions, and evolving customer behavior.
Insurers should monitor:
- Model accuracy and relevant performance metrics.
- False-positive and false-negative rates.
- Data quality and input distribution.
- Model drift.
- Output consistency.
- Workflow completion and failure rates.
- Human override rates.
- Escalation volumes.
- Consumer complaints and reported incidents.
- Third-party service changes.
Monitoring should also consider whether human reviewers are consistently challenging questionable recommendations.
A very low override rate is not necessarily evidence of a highly accurate AI system. It could indicate reviewer over-reliance, inadequate training, or insufficient review time.
Practical recommendation: Establish monitoring thresholds and escalation procedures. Material deviations should trigger investigation, additional testing, restricted operation, or suspension where necessary.
What Should an Insurance AI Audit Trail Contain?
A useful AI audit trail should allow an authorized reviewer to reconstruct the relevant workflow without depending on informal explanations from the original developer or operator.
The following example illustrates a claims workflow.
Example: AI-Assisted Claims Triage
A P&C insurer receives a property damage claim.
The AI workflow extracts information from the claim submission, checks relevant policy records, identifies missing information, and recommends a review category.
| Workflow stage | Activity | Evidence retained |
|---|---|---|
| 1. Claim intake | Claim is registered | Claim ID, timestamp, source channel |
| 2. Document processing | AI extracts claim details | Document references, extraction output, validation results |
| 3. Policy retrieval | Relevant policy information is retrieved | Policy version, source reference, retrieval timestamp |
| 4. AI analysis | System generates a triage recommendation | Model version, configuration, input references, output |
| 5. Risk and rule checks | Business rules and validation checks run | Rule versions, validation results, exception details |
| 6. Human review | Claims professional reviews the recommendation | Reviewer ID, decision, comments, timestamp |
| 7. Workflow action | Claim is routed to the appropriate team | Final routing action, status, execution record |
| 8. Monitoring | Outcome is included in operational monitoring | Performance indicators, exception and override records |
This approach makes the process traceable from intake through final routing.
If a reviewer later questions why the claim was routed to a particular team, the insurer can examine the source information, AI output, applicable rules, and human review record.
The same pattern can be adapted for underwriting, customer service, fraud investigation, and other AI-enabled processes.
Designing Meaningful Human Oversight
A human approval step does not automatically create meaningful oversight.
If employees approve hundreds of AI recommendations without sufficient time, evidence, or authority to challenge them, the process may create the appearance of control without delivering effective supervision.
Insurers should design human oversight around the following principles.
1. Give Reviewers Sufficient Information
Reviewers need access to the underlying evidence, relevant business rules, and the reasoning or supporting factors available from the system.
An unexplained AI score should not be the only basis for a consequential decision.
2. Give Reviewers Real Authority
Employees should have the ability to reject, modify, or escalate an AI recommendation.
If the workflow technically requires human approval but does not permit meaningful intervention, oversight is weak.
3. Match Review Requirements to Risk
Not every AI-generated output requires the same level of review.
Internal summarization may require periodic sampling. A consequential consumer-impacting recommendation may require a qualified person to review it before the action proceeds.
4. Train Employees to Recognize AI Limitations
Employees should understand:
- What the AI system is designed to do.
- Which data it uses.
- What its known limitations are.
- When its output may be unreliable.
- How to recognize unsupported or incorrect information.
- How to challenge or escalate a recommendation.
5. Monitor Automation Bias
Automation bias occurs when people give excessive weight to automated recommendations and fail to independently evaluate the evidence.
Insurers should monitor review behavior, train employees to question questionable outputs, and make override processes practical.
6. Maintain Appropriate Staffing and Review Capacity
Human oversight can fail when review volumes exceed available capacity.
Organizations should monitor queue sizes, review time, escalation delays, and approval workloads.
A control that cannot operate effectively under actual business volumes is not a reliable control.
Governance Frameworks and Regulatory Considerations for Insurance AI
Insurance companies should align their AI governance programs with applicable insurance laws, regulatory expectations, recognized risk management frameworks, and internal enterprise policies.
Three important references are the NAIC Model Bulletin, NIST AI Risk Management Framework, and the European Union AI Act.
1. NAIC Model Bulletin on the Use of AI Systems by Insurers
The NAIC adopted its Model Bulletin in December 2023.
It reminds insurers that decisions or actions made or supported by AI must comply with applicable insurance laws and regulations, including requirements concerning unfair trade practices and unfair discrimination.
The bulletin discusses expectations around a written AI Systems Program and documentation that regulators may request. Relevant areas include:
- AI governance and risk management.
- Data sources and data lineage.
- Data quality and suitability.
- Model validation and testing.
- Bias analysis.
- Performance monitoring.
- Third-party AI systems.
- Vendor due diligence and contractual controls.
- Documentation of auditing and model drift.
2. NIST AI Risk Management Framework
The NIST AI Risk Management Framework provides a voluntary framework for managing risks associated with AI systems.
Its four core functions are:
| NIST function | Purpose | Insurance application |
|---|---|---|
| Govern | Establish organizational policies, accountability, and oversight | AI governance committee, ownership, approval policies |
| Map | Understand AI context, intended use, and potential risks | Identify consumer impact, data sources, and workflow dependencies |
| Measure | Assess AI performance, reliability, and risks | Validation, bias testing, monitoring, and evaluation |
| Manage | Prioritize and respond to identified risks | Human review, escalation, remediation, and system restrictions |
The framework emphasizes continuous risk management throughout the AI lifecycle.
3. EU AI Act and Human Oversight
The European Union AI Act establishes requirements for high-risk AI systems, including risk management, documentation, record-keeping, and human oversight.
Article 14 addresses human oversight and requires high-risk AI systems to be designed so that people can effectively oversee their operation.
Article 14 also addresses the ability of assigned personnel to understand system capabilities and limitations, monitor operation, interpret outputs, disregard or override outputs, and intervene where appropriate.
Importantly, not every insurance AI application is automatically classified as high-risk under the Act. EIOPA identifies AI systems used for risk assessment and pricing in life and health insurance as high-risk under the relevant AI Act classification. The applicability of requirements should be assessed against the specific system, purpose, and legal context.
Practical recommendation: Use these frameworks as inputs to an enterprise AI control framework, but have legal and compliance teams validate jurisdiction-specific obligations, effective dates, and applicability before deployment.
Third-Party AI and Vendor Governance
Insurance companies do not always develop AI systems internally. They may use models, data, software, and AI services supplied by technology vendors.
This introduces additional governance challenges.
An insurer may depend on a third-party AI service for claims summarization, underwriting insights, fraud detection, or customer service without having direct access to the underlying model.
The organization still needs sufficient information to understand and govern the system’s use.
Key Vendor Governance Requirements
Insurers should evaluate:
- Vendor AI capabilities and intended use.
- Model documentation and validation evidence.
- Data sources and data provenance.
- Data privacy and security controls.
- Model update and version-management processes.
- Performance monitoring and drift management.
- Incident reporting and escalation.
- Subprocessor and subcontractor dependencies.
- Data retention and deletion arrangements.
- Audit and regulatory cooperation provisions.
- Business continuity and exit arrangements.
Contractual agreements should define responsibilities for security, data handling, incident notification, model changes, and access to relevant documentation.
For generative AI services, insurers should also assess whether submitted information may be retained or used to improve provider models, according to the applicable contractual and technical arrangements.
Practical recommendation: Maintain a third-party AI inventory and link vendor assessments, contractual controls, validation evidence, and ongoing performance reviews to the relevant internal AI use case.
How Generative AI and AI Agents Change Auditability Requirements
Traditional predictive models and generative AI systems create different audit challenges.
A predictive model may produce a classification, score, or probability based on defined input features. A generative AI system may retrieve documents, interpret natural-language instructions, generate content, call external tools, and produce different outputs for similar requests.
AI agents add another layer because they can perform multi-step tasks and interact with enterprise systems.
As a result, traditional model logs alone may not be sufficient.
Audit Requirements for Generative AI
For generative AI workflows, insurers should consider recording:
- Model and deployment version.
- Prompt and instruction version.
- User request or task context, subject to privacy controls.
- Retrieved document references.
- Knowledge-base version.
- Tool calls and API interactions.
- Generated output.
- Relevant validation results.
- Human edits and approvals.
- Final business action.
Where possible, organizations should retain the evidence needed to reconstruct the information available to the system at the time of execution.
For RAG-based applications, document identifiers, retrieval metadata, source versions, and access permissions are especially important.
Audit Requirements for AI Agents
AI agents may interact with policy platforms, claims applications, customer systems, and enterprise APIs.
An agent might retrieve a policy record, summarize a claim, prepare a draft communication, and initiate a permitted workflow action.
A controlled agent architecture should include:
- Defined agent identity.
- Approved task scope.
- Least-privilege access.
- Tool and API allowlists.
- Permission checks for each action.
- Human approval for designated high-impact actions.
- Execution limits and timeout controls.
- Transaction and action logs.
- Exception handling and rollback mechanisms where technically possible.
For example, an AI agent may be allowed to prepare a claims summary and recommend routing. It may not have permission to make a restricted claims decision or modify sensitive policy information without the required authorization.
Practical recommendation: Treat AI agents as workflow participants with explicitly defined permissions, not as unrestricted digital employees.
Reference Architecture: Auditable AI Workflow for Insurance
A scalable architecture should connect AI capabilities with business systems, governance services, human review, and centralized audit evidence.
The following logical architecture illustrates the major components.
Layer 1: Enterprise Data and Business Systems
Sources include:
- Policy administration systems.
- Claims management platforms.
- Billing and finance systems.
- Underwriting applications.
- Customer relationship management systems.
- Enterprise document repositories.
- External data providers.
- Approved knowledge bases.
These systems provide the business information required by the AI workflow.
Layer 2: Data Integration and Governance
This layer provides:
- Secure data ingestion.
- Data validation.
- Data classification.
- Access controls.
- Data lineage.
- Master and reference data management.
- Approved data products.
It ensures that AI applications use authorized and appropriately governed information.
Layer 3: AI Services and Model Management
This layer includes:
- Predictive models.
- Generative AI services.
- RAG pipelines.
- AI agents.
- Model registry.
- Prompt and configuration management.
- Model evaluation.
- AI safety and validation controls.
Each execution should be associated with identifiable model and configuration information.
Layer 4: Workflow Orchestration and Human Review
This layer manages:
- Business process execution.
- Decision rules.
- Approval gates.
- Exception handling.
- Escalation.
- Human review queues.
- Authorized actions.
- Workflow status.
The orchestration layer determines what an AI system may recommend, which actions it may perform, and when human authorization is required.
Layer 5: Audit, Monitoring, and Governance
Cross-cutting capabilities include:
- Centralized audit logging.
- Model and workflow monitoring.
- Data lineage.
- Access and activity monitoring.
- Human intervention records.
- Incident management.
- Compliance reporting.
- Vendor governance.
- Retention and evidence management.
Layer 6: Business Applications and Reporting
The final layer delivers controlled AI-enabled services to:
- Underwriters.
- Claims professionals.
- Fraud investigators.
- Customer service teams.
- Actuarial teams.
- Finance and risk functions.
- Enterprise leadership.
Architecture principle: AI services should not independently control consequential business processes. Workflow orchestration, authorization, and governance should determine which actions can be performed and when human intervention is required.
Implementation Roadmap: Building Auditable AI Workflows Step by Step
Insurers should implement auditable AI workflows incrementally, starting with a clearly defined use case and expanding the control framework as the organization gains experience.
| Phase | Focus | Key activities | Expected outcome |
|---|---|---|---|
| Phase 1: Discover | Identify existing AI usage | Inventory models, vendors, workflows, and business owners | Enterprise AI use-case inventory |
| Phase 2: Assess | Understand risk and impact | Classify use cases, identify legal requirements, assess data and consumer impact | Risk-based control requirements |
| Phase 3: Design | Define workflow controls | Establish audit events, approval gates, reviewer roles, and escalation paths | Auditable workflow design |
| Phase 4: Implement | Build technical capabilities | Integrate model registry, logging, orchestration, access control, and human review | Controlled AI workflow |
| Phase 5: Validate | Test effectiveness | Evaluate model performance, fairness, security, traceability, and human oversight | Deployment readiness evidence |
| Phase 6: Operate | Monitor production behavior | Track performance, overrides, incidents, drift, and review effectiveness | Continuous oversight |
| Phase 7: Scale | Expand across business functions | Reuse controls, templates, and governance patterns | Enterprise AI governance capability |
Recommended Pilot: AI-Assisted Claims Triage
A practical starting point is an AI-assisted claims triage workflow.
The pilot can be structured as follows:
- Select a specific claims process and define its approved AI use.
- Identify the source systems and data permitted for processing.
- Define the AI system’s role, boundaries, and prohibited actions.
- Configure the workflow to extract and summarize claim information.
- Establish validation rules and exception thresholds.
- Create a human review interface for designated decisions.
- Capture model versions, source references, outputs, approvals, and final actions.
- Test incorrect outputs, missing data, and unusual cases.
- Evaluate reviewer performance and override behavior.
- Obtain business, risk, compliance, and technology approval before production use.
This pilot can validate both the AI capability and the governance mechanisms required to operate it responsibly.
KPIs to Measure Auditable AI Workflow Effectiveness
AI governance should be measured through operational performance, model reliability, human oversight, and audit readiness.
A useful KPI framework includes:
| KPI | What it measures | Why it matters |
|---|---|---|
| Audit trail completeness | Percentage of required workflow events captured | Indicates traceability |
| Human review compliance | Percentage of workflows meeting required review controls | Measures oversight execution |
| Override rate | Percentage of AI recommendations modified or rejected | Helps identify potential model or workflow issues |
| Model error rate | Frequency of incorrect outputs against defined evaluation criteria | Measures model reliability |
| Exception rate | Percentage of workflows requiring exception handling | Identifies operational complexity |
| Review turnaround time | Time taken for required human review | Measures operational efficiency |
| Unauthorized action incidents | Actions attempted or performed outside approved permissions | Measures workflow security |
| Data quality compliance | Percentage of inputs meeting defined quality requirements | Measures input reliability |
| Model drift incidents | Number of material performance or data drift events | Supports ongoing model monitoring |
| Audit evidence retrieval time | Time required to produce evidence for a selected workflow | Measures audit readiness |
| Third-party assessment coverage | Percentage of relevant vendors with completed AI risk reviews | Measures vendor governance |
Targets should be based on the insurer’s initial operating baseline, business risk, and control requirements.
A low override rate should not automatically be treated as proof of good model performance. It should be evaluated alongside accuracy, reviewer behavior, case complexity, and the quality of human review.
Common Mistakes Insurance Companies Should Avoid
1. Treating Human Approval as a Complete Governance Strategy
A single approval button does not guarantee that the reviewer understands the recommendation or can challenge it.
Better approach: Provide supporting evidence, relevant context, review authority, and documented intervention options.
2. Recording Only Technical Logs
API requests and model responses do not provide a complete picture of business decision-making.
Better approach: Connect technical events with workflow IDs, business records, human actions, and final outcomes.
3. Allowing AI to Execute Actions Beyond Its Approved Scope
AI agents may gain access to business tools that can modify records or initiate transactions.
Better approach: Use least-privilege access, tool allowlists, explicit authorization, and approval gates for designated actions.
4. Ignoring Third-Party AI Risks
An insurer may use an AI service without understanding its model updates, data handling, or validation practices.
Better approach: Establish vendor due diligence, contractual requirements, monitoring, and documented oversight.
5. Assuming Model Accuracy Guarantees Fairness
A model may achieve strong aggregate performance while producing uneven outcomes across relevant customer groups or business segments.
Better approach: Conduct appropriate fairness assessments, monitor relevant outcomes, and involve qualified risk and compliance professionals.
6. Failing to Monitor Human Behavior
Reviewers may become overly dependent on AI recommendations or approve outputs without sufficient examination.
Better approach: Train reviewers, monitor override and review patterns, and evaluate the effectiveness of human intervention.
7. Ignoring Model and Prompt Changes
A model, prompt, retrieval configuration, or business rule change may alter workflow behavior.
Better approach: Maintain version control, change approval, regression testing, and production monitoring.
8. Treating Auditability as a Post-Deployment Activity
Adding audit logging after the workflow is operational may leave important evidence unavailable.
Better approach: Define audit requirements during workflow design and validate them before production deployment.
Future Trends: The Next Stage of AI Governance in Insurance
Insurance AI governance will continue to evolve as organizations move from standalone models toward connected generative AI applications and autonomous agents.
1. Greater Use of AI Agents With Controlled Permissions
AI agents will increasingly support multi-step insurance operations. This will increase the importance of identity management, tool permissions, action-level audit logs, and human authorization.
2. Continuous AI Monitoring and Evaluation
Insurers will need to monitor more than model accuracy. Workflow reliability, data quality, human intervention, security, and consumer outcomes will become important parts of operational AI monitoring.
3. More Detailed Evidence for Generative AI Workflows
Generative AI systems will require better tracking of prompts, model versions, retrieval sources, tool calls, and output validation.
This will become particularly important when AI-generated information influences consequential business processes.
4. Integration of AI Governance Into Enterprise Architecture
AI governance will increasingly become part of enterprise architecture rather than a separate compliance activity.
Model registries, data governance, workflow orchestration, access management, monitoring, and audit systems will need to work together.
5. Greater Focus on Human-AI Collaboration
The emphasis will move from simply asking whether a task can be automated to determining which activities benefit from AI assistance, which require human judgment, and how both can operate within a controlled process.
For insurers, the long-term opportunity is to improve operational efficiency while preserving accountability and customer trust.
Conclusion: Make Every AI Decision Traceable and Accountable
AI can improve insurance operations, but scaling it responsibly requires more than deploying models and automating tasks. Insurers need to understand how AI systems operate, what information influences their outputs, how people review recommendations, and who authorizes the resulting actions.
Auditable AI workflows provide this foundation by connecting data provenance, model and prompt versioning, workflow orchestration, human approvals, audit logging, and continuous monitoring.
Human oversight must also be meaningful. Reviewers need the information, authority, expertise, and time required to challenge AI recommendations. High-impact actions should follow clearly defined approval and escalation processes.
For insurance companies, the path forward is to build governance into AI workflows from the beginning—not treat it as a separate compliance layer added after deployment.
Techment’s capabilities across Enterprise AI, AI Strategy, Data Engineering, RAG, AI Agents, Cloud Modernization, and Enterprise Software Engineering can help insurers design and implement governed AI workflows that connect enterprise data, intelligent automation, and human decision-making.
The objective is not simply to make AI faster. It is to make AI operationally reliable, traceable, and accountable.
Frequently Asked Questions
1. What is an auditable AI workflow in insurance?
An auditable AI workflow is an AI-enabled insurance process that maintains traceable records of its inputs, data sources, model versions, AI outputs, human reviews, approvals, and final actions. It allows insurers to reconstruct how a workflow operated and determine who was responsible for consequential decisions.
2. Why do insurance companies need human oversight for AI?
Insurance AI can influence underwriting, pricing, claims, fraud investigations, and customer interactions. Human oversight helps qualified employees evaluate AI recommendations, identify errors, challenge unsupported outputs, and authorize actions according to business and regulatory requirements.
3. What is the difference between human-in-the-loop and human-on-the-loop AI?
Human-in-the-loop requires a person to review or approve a defined AI output before a workflow proceeds. Human-on-the-loop involves a person supervising an automated process and intervening when necessary. The appropriate approach depends on the risk and intended use of the AI system.
4. What should an AI audit trail include?
An AI audit trail should include workflow identifiers, relevant input references, data provenance, model and configuration versions, AI outputs, validation results, human reviewer details, approvals, overrides, timestamps, and final actions. It should also include relevant exceptions and monitoring records.
5. How can insurers make generative AI auditable?
Insurers can make generative AI auditable by recording model and prompt versions, input context, retrieved source references, knowledge-base versions, tool calls, generated outputs, validation results, human interventions, and final actions. Sensitive information should be handled under appropriate privacy, access, and retention controls.
6. How can insurers measure the effectiveness of human oversight?
Insurers can monitor review compliance, override rates, escalation frequency, review turnaround time, reviewer training, audit trail completeness, and the quality of human decisions. These measures should be evaluated together because a low override rate alone does not prove that oversight is effective.
7. How can insurance companies prevent AI agents from taking unauthorized actions?
Insurers can control AI agents through least-privilege access, approved tool and API lists, task boundaries, authorization checks, transaction logs, execution limits, and human approval gates. Consequential or irreversible actions should require the appropriate authorization under the organization’s control framework.
Related Reads
- From Chatbots to Agents: The AI Maturity in Insurance
- AI-Ready Enterprise Checklist with Microsoft Fabric
- AI-Powered Risk Assessment in Insurance: Models & Use Cases
- RAG for Insurance: How Retrieval-Augmented AI Speeds Up Claims Processing
- Microsoft Fabric for Insurance Carriers: A Reference Architecture
- AI in Insurance: Benefits, Use Cases in 2026